Industrial Cybersecurity Knowledge: OT Protection, Network Segmentation, Monitoring and Risk Assessment
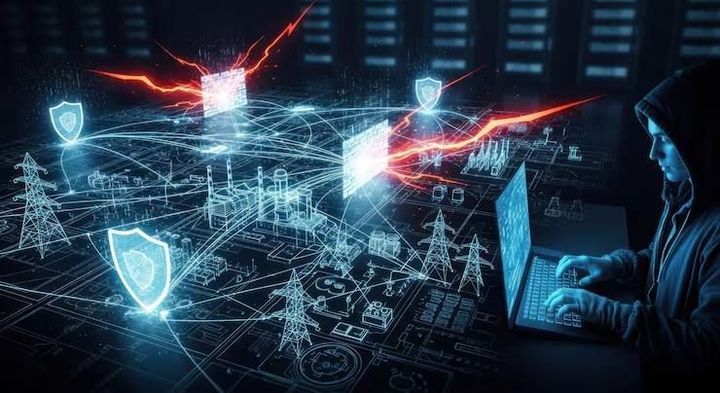
Industrial cybersecurity is the practice of protecting the digital systems that control, monitor, and support physical industrial operations. It is closely connected with operational technology (OT), which includes programmable logic controllers (PLCs), supervisory control and data acquisition (SCADA) systems, distributed control systems (DCS), industrial sensors, robotic equipment, and other technologies used in factories, utilities, transportation, energy, and processing facilities.
Traditional IT security mainly focuses on computers, applications, accounts, and information. OT protection has a wider operational concern because a cyber incident can affect physical processes as well as digital information. A disruption involving an industrial control system could interfere with production, equipment operation, safety processes, or the availability of an important facility. ISA/IEC 62443 was developed as a cybersecurity framework for industrial automation and control systems and addresses people, processes, technology, risk assessment, and security throughout the system lifecycle.
Industrial environments have changed as factories and infrastructure have become more connected. Systems that once operated within isolated networks may now exchange information with enterprise networks, remote monitoring platforms, cloud systems, engineering workstations, and external connections. This connectivity can improve visibility and operational coordination, but it also creates additional pathways that need to be understood and controlled.
Industrial cybersecurity therefore combines several areas, including asset identification, network segmentation, access control, vulnerability management, monitoring, incident response, and risk assessment. The objective is to understand how industrial systems operate and establish security controls without unnecessarily interfering with physical processes.
Importance
Industrial cybersecurity matters because many everyday activities depend on industrial and critical infrastructure. Manufacturing plants produce components and products, power facilities support electrical systems, water facilities manage essential resources, and transportation infrastructure relies on interconnected control technologies.
A cybersecurity incident in an industrial environment can have different consequences from an incident involving an ordinary office computer. Potential effects may include interrupted production, incorrect process information, unauthorized changes to equipment settings, loss of monitoring visibility, or delays in restoring operations.
OT environments also have characteristics that make protection more complex. Some equipment may remain operational for many years, while replacing or updating a controller can require careful testing. Certain systems may depend on older operating environments or specialized communication protocols. Security controls therefore need to consider operational requirements as well as cybersecurity concerns.
Key areas of industrial cybersecurity
Several areas commonly form part of an industrial cybersecurity program:
- Asset visibility: Identifying controllers, servers, workstations, network devices, sensors, and communication paths.
- OT protection: Separating and protecting systems responsible for physical processes.
- Network segmentation: Dividing networks into controlled zones so that unnecessary communication is restricted.
- Monitoring: Observing network activity, system events, authentication attempts, and unusual behavior.
- Risk assessment: Examining assets, threats, vulnerabilities, possible consequences, and existing safeguards.
- Access control: Limiting system access according to legitimate operational responsibilities.
- Incident response: Establishing procedures for identifying, containing, investigating, and recovering from cybersecurity incidents.
These areas are connected rather than independent. For example, effective network segmentation depends on knowing which systems need to communicate, while monitoring becomes more useful when the normal communication patterns of those systems are understood.
Why network segmentation matters
Network segmentation separates different groups of systems into controlled network areas. In an industrial environment, an organization may separate corporate IT systems, manufacturing networks, control networks, safety-related systems, and external connections.
Segmentation can reduce unnecessary pathways between systems. Firewalls, controlled gateways, access rules, and demilitarized zones (DMZs) can be used to regulate communication between network areas. ISA/IEC 62443 materials specifically include zones, conduits, firewalls, DMZs, access control, intrusion detection, and related controls within industrial cybersecurity design approaches.
Recent Updates
From 2024 through 2026, industrial cybersecurity has increasingly focused on structured security programs, software and hardware visibility, vulnerability management, and risks created by growing connectivity.
One notable development was the publication of ANSI/ISA-62443-2-1-2024, which updated requirements for establishing, implementing, maintaining, and continually improving an industrial automation and control systems security program. The update also introduced changes to the organization of security requirements and maturity-related evaluation concepts.
Another development was ISA-TR62443-2-2-2025, which provides guidance concerning security protection schemes for industrial automation and control systems. The document addresses how security mechanisms and procedures can be developed, validated, operated, and maintained within an industrial environment.
Software and component visibility has also received greater attention. CERT-In published technical guidelines covering software bills of materials and related component inventories, including SBOM, QBOM, CBOM, AIBOM, and HBOM concepts. These approaches can help organizations understand what software, hardware, and technology components exist within their environments.
Artificial intelligence is another developing area. During 2026, CERT-In published guidance concerning AI-assisted vulnerability exploitation and AI-accelerated vulnerability protection and response. This reflects the broader cybersecurity trend toward considering how AI can affect both defensive activities and emerging attack techniques.
Current industrial monitoring trends
Monitoring is also moving beyond simple network availability checks. Organizations increasingly examine communication patterns, authentication events, configuration changes, unusual commands, and interactions between IT and OT environments.
The purpose is not necessarily to inspect every event manually. Instead, monitoring systems can establish an understanding of expected activity and help security teams identify events that require further investigation. In OT environments, monitoring approaches need to account for operational requirements because unexpected changes to equipment or communication can have physical consequences.
Laws or Policies
In India, industrial cybersecurity is influenced by the Information Technology Act, 2000, CERT-In directions, and arrangements for protecting critical information infrastructure. The Information Technology Act provides a legal framework for protected computer systems and critical information infrastructure. Section 70 allows specified computer resources affecting critical information infrastructure to be declared protected systems, while Section 70A provides for a national nodal agency concerning critical information infrastructure protection.
CERT-In operates under Section 70B of the Information Technology Act and has responsibilities that include collecting and analyzing information about cyber incidents, issuing alerts and guidance, coordinating incident response, and supporting cybersecurity practices.
CERT-In's 2022 cybersecurity directions established requirements relating to information security practices, incident prevention, response, and reporting. Organizations covered by applicable requirements need to consider these directions when developing their cybersecurity processes.
CERT-In has also continued publishing sector and organization-focused guidance. Recent publications include guidance for smart city infrastructure, cybersecurity audits, and cybersecurity controls for micro, small, and medium enterprises. These documents illustrate the continuing development of cybersecurity guidance across different types of digital infrastructure.
The Digital Personal Data Protection Rules, 2025 are another relevant development for organizations that process personal data. Their relevance to an industrial environment depends on what personal information the organization handles and which provisions apply. They are therefore related to data protection rather than being an OT-specific security framework.
Organizations may also need to consider sector-specific rules, contractual requirements, internal security policies, and requirements applicable to designated critical infrastructure. The exact obligations depend on the organization, industry, systems involved, and applicable legal classification.
Tools and Resources
Several established frameworks, standards, and resources can help readers understand industrial cybersecurity.
Industrial cybersecurity resources
ISA/IEC 62443 is a major reference for industrial automation and control systems cybersecurity. It covers terminology, security programs, risk assessment, system requirements, component requirements, and lifecycle considerations.
NIST cybersecurity publications provide general frameworks and technical guidance that can be applied to many organizations. NIST resources can help explain concepts such as cybersecurity risk management, asset identification, access control, incident response, and continuous monitoring.
MITRE ATT&CK for ICS provides a knowledge base describing tactics and techniques associated with industrial control system environments. It can help readers understand how different attack behaviors may occur across an industrial environment.
CERT-In is an important Indian government resource for cybersecurity advisories, guidelines, incident information, and applicable directions. Its publications can help organizations understand developments relevant to cybersecurity practices in India.
Common assessment areas
A basic industrial cybersecurity risk assessment can organize information into several categories:
| Assessment Area | Example Information | Purpose |
|---|---|---|
| Assets | PLCs, SCADA servers, HMIs, sensors | Understand what needs protection |
| Connections | IT, OT, remote and external links | Identify communication pathways |
| Vulnerabilities | Outdated software, weak access controls | Identify potential weaknesses |
| Threats | Malware, unauthorized access, misuse | Understand possible attack paths |
| Impact | Production, safety, availability | Understand possible consequences |
| Controls | Firewalls, segmentation, monitoring | Record existing safeguards |
| Recovery | Backups, procedures, restoration plans | Understand recovery capability |
Risk assessment should consider both cybersecurity and operational consequences. A vulnerability on an isolated test system may have different implications from a similar weakness on a controller connected to a production process.
A practical assessment also needs accurate asset inventories and network diagrams. Without a clear understanding of what equipment exists and how systems communicate, it becomes harder to determine which connections require restrictions or which events may represent unusual activity.
FAQs
What is industrial cybersecurity?
Industrial cybersecurity is the protection of operational technology, industrial control systems, networks, equipment, and related digital components from unauthorized access, disruption, manipulation, and other cybersecurity risks. It combines technical controls with operational procedures and risk management.
Why is OT protection different from normal IT security?
OT protection must consider physical processes and operational continuity in addition to information security. Industrial equipment may have long operating lifecycles, specialized protocols, and strict availability requirements, so security changes often need careful evaluation before implementation.
How does network segmentation improve industrial cybersecurity?
Network segmentation divides an environment into controlled network areas and limits unnecessary communication between them. It can reduce pathways between corporate IT, industrial control systems, external connections, and other network zones when designed appropriately.
What is involved in an industrial cybersecurity risk assessment?
An industrial cybersecurity risk assessment generally involves identifying assets, understanding network connections, examining vulnerabilities and threats, considering potential consequences, and reviewing existing controls. Standards such as ISA/IEC 62443 include risk assessment concepts for industrial automation and control environments.
What tools can help with OT monitoring?
OT monitoring can use network visibility platforms, intrusion detection technologies, centralized event collection, asset inventories, vulnerability databases, and industrial protocol analysis tools. The appropriate approach depends on the architecture, equipment, operational requirements, and monitoring objectives of the environment.
Conclusion
Industrial cybersecurity combines OT protection, network segmentation, monitoring, access control, and risk assessment to address cybersecurity risks in connected industrial environments. Recent developments have placed greater attention on structured security programs, component visibility, industrial control system standards, and emerging technology-related threats. In India, the Information Technology Act and CERT-In directions form important parts of the broader cybersecurity framework, while specific organizations may also face additional sectoral requirements. Industrial cybersecurity is therefore an ongoing discipline involving technology, processes, people, and an understanding of the physical systems being protected.